Diff
-
Posts
551 -
Joined
-
Last visited
-
Days Won
1
Content Type
Profiles
Forums
Blogs
News
Store
Everything posted by Diff
-
theory on Open Source Anti-cheat as a mod (Not the current drama)
Diff replied to Zvengks's topic in Discussion
Wait, can we confirm this? Is it not all server-sided? I know the server is naive but I didn't think it farmed out actual RNG calculations out to the clients. Runs a little contrary to what I thought I knew about the server/client split, but I do go out of my way to avoid the networking portions. -
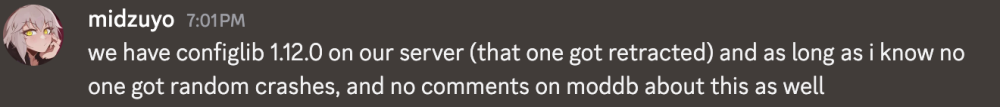
Hey I put together a thing tonight because I was getting more curious about why ConfigLib wouldn't have crashed playerlists. Still investigating it, but on my way I made this: https://mods.vintagestory.at/notconfiglib It's a mod that will print in chat when you join whether or not the current loaded set of mods would have crashed with Config lib on a multiplayer server. If you check the Git history you can see it came from a file that was basically just AdditionalStuff.cs stuffed into a ModSystem. Since that initial commit, it's been stripped down, defanged, and spruced up, but still contains the same checks. Test it out if you're curious, let me know if anything blows up. On my machine it properly aggros at CNC and URL Radio but oddly doesn't aggro at playerlists... That kind of aligns with the total lack of crash reports for that mod, but I don't know why that would be yet. EDIT: PlayerLists doesn't crash because it's actually not obfuscated enough. Added some debugging to NotConfigLib and it reports that PlayerLists only has 20.8% short names the way ConfigLib calculates it, not the required 22%. For reference, CNC is 29% and URL Radio has 35%. That opens the question back up, is it a different playerlist mod that crashes? None of the other forks I checked had any obfuscated code at all.
-
@Thorfinn Found it. It's actually "playerlists" not "playerlist." There currently is no "playerlist," apparently there was some interesting drama going on with the original and its descendants. But after "playerlists" forked off from the original, it started obfuscating, likely related to being "merged with my own security addon" mentioned in the description. So, same thing as the other two. This is by far the most popular of the false positives, with 3500 downloads on the latest version. Oddly nobody in the comments complaining about crashes. Both of the other mods had people in the comments, and this one should have been ripe for it with it being explicitly multiplayer-focused. Not sure what to make of that. EDIT: Author confirms no reports of crashes, or crashes on their own server running the mod with one of the retracted versions of ConfigLib. I don't see how it escaped ConfigLib's wrath.
-
Separate things. Short names are just what ConfigLib hunted for and targeted. And specifically, short class and type names. Short variable names were beyond what it was looking at (Assembly.GetTypes()). The cheat mod, separate from its short names, operated by exploiting the fact that the server just kinda trusts clients to tell the truth. The cheat mod lied and said "why yes, I mined all 470 blocks in the vicinity in the past 0.1 seconds." "Hey, server, I just killed everything within a 10 block radius." The server doesn't check to make sure that's sane or possible.
-
Believe only internal references get scrambled. So like instead of CheatModSystem and CheatModDialog and CheatModConfig, you get a, A, and b. URL Radio for instances has a lot of normal names and only an interior core gets scrambled. Obfuscation like that makes it really difficult to fingerprint a chunk of code, especially when obfuscated names can change version to version. Today's q might be tomorrow's zN. If they had used longer names, or names that had a less consistent scheme, it could have been even more difficult to latch onto.
-
I haven't looked at playerlist yet, planning to this afternoon. The first two angered ConfigLib by being obfuscated. More than 22% of their types were 2 chars or less. That's likely the case for the third, but there's a small chance of other shenanigans biting here.
-
Those accounts are different beasts entirely. You can't sneak malware through code review. You can maybe sneak a vulnerability through code review, but that's primarily in memory-unsafe languages like C and C++. C# can't have memory unsafety holes accidentally poked in it just because you weren't paying close enough attention. XZ didn't sneak past code review. It was done by a maintainer where there was no code review at all. I'm deeply confused by this statement, a conflict in what way? Developer modding their own game with their own personal ideas without integrating them into main sounds like a great way to toy and experiment in a low-stakes way that can be trashed at a moment's notice.
-
theory on Open Source Anti-cheat as a mod (Not the current drama)
Diff replied to Zvengks's topic in Discussion
What I'm not understanding is, who cares to tamper with it if it's not doing any additional detection or prevention? It's not doing anything the server couldn't already do, so there's no value to a cheater to even pay attention to it. They'll still get away with it until it's reviewed (which will be after the damage is done and likely after they've had their fun). And the other thing I don't understand is actually the same thing flipped, what's the gain vs a hypothetical anti-cheat that was purely server-side with no client-side component? Either they cheat and the server-recorded demo records the cheat and they get caught, or they don't cheat and fight fair and it doesn't matter, and that's it, there is no third thing. It just looks like a server side anticheat (which I like) with extra steps. In your poker analogy, in VS, the dealer does write all the bets. If the server can't be trusted then everyone's screwed. The server contains the only true authoritative record of what is happening in the world at any point in time. It's deeply centralized, and this client-side model doesn't make sense when the necessary data is already centralized. -
theory on Open Source Anti-cheat as a mod (Not the current drama)
Diff replied to Zvengks's topic in Discussion
If the demo file capture by the client doesn't matter, why is it capturing it? If the server is also monitoring all the actions and has to compare them, what's the point of sending everything twice? Sounds even more like it should just stay server-side and then your client side can never be defeated. So you've attested that the mod is installed, or that someone merely copied the handshake from the decompiled DLL or the open-source implementation. If the client isn't doing anything the server isn't already doing, I'm unclear what is gained. The client isn't seeing or sending anything extra, so it doesn't harm a cheater at all to just let it be. An LLM requires a massive amount of processing power. A neural network built for a task can be small enough to run on a microcontroller. In like 2016 I built one to detect bass kicks in music based on a small amount of messy audio data that I hand labeled in an hour or two. Basic machine learning predates LLMs and is a time tested technique for certain kinds of problems. I would never want to directly ban someone based on the output of one of these things, but it'd be certainly useful to flag them for manual review in your demo reel when they hit a threshold of confidence. -
theory on Open Source Anti-cheat as a mod (Not the current drama)
Diff replied to Zvengks's topic in Discussion
That's a nontrivial problem that large open source distros with large amounts of corporate funding took years to solve and complete the work on. Most of them still don't bother. It's not a setting they didn't turn on, it's the computer in its natural state, and it's the same situation that every game modding community out there finds itself in. You compile the same mod twice on two different computers, without taking explicit action to prevent it, you will have two different DLLs built from the same source, both equally correct. -
Weird, with nicely rendered fat, the only other gotcha I see is that the rod can't be gold, silver, cupronickel, or electrum but your rod doesn't look like any of those. Like you said, hammer and chisel shouldn't be it either. Those only need 30-40 durability. I'm stumped.
-
I'm not at my computer, but the one thing I notice looking at the recipe is that the fat must be rendered. Is yours?
-
Do you know who's on third? People have mentioned it indirectly but I only know Caves N Caverns and URL Radio by name.
-
theory on Open Source Anti-cheat as a mod (Not the current drama)
Diff replied to Zvengks's topic in Discussion
These demo files could be (and maybe should be) captured on the server side. A cheat mod knows if it's about to do something illegal and can just not include that in the demo that's sent to the server. I don't see anything here that doesn't have visibility on the server side, and anything that is going to impact other players (excluding leaking info like Xray cheats) is going to have to loop the server in on what's going on. Capturing it on the client side seems to only leave it open to be tampered with. Cheat mod doesn't have to re-implement diffie-hellman if it just selectively blinds the anticheat when it needs it to look the other way. -
Nailed it. Right, if we take Maltiez at his outdated word, it was never about protection. It was about frustrating the person developing cheats until they stopped developing cheats. In the game, there is a function "TryAttackEntity" that is used to attack things. AdditionalStuff tells it the thing we're trying to attack is ourselves. Which is probably legitimately used sometimes, I'm thinking using a temporal gear to restore stability likely does the same thing. But it is absolutely more of an annoyance. Player likely winds up thinking it's just delayed fall damage or a hidden bowtorn or something.
-
Huh, you're right. I have two copies of AdditionalStuff.cs, one from Maltiez's discord message and the one I yanked myself out of 1.10.9. I was referencing the decompiled version from 1.10.9, I'll attach it here as well. AdditionalStuff.cs.txt
-
Which ones are you thinking of? People have managed to slip evil code into the Linux kernel before. And of course there's the XZ incident. But these really are different beasts. In the XZ incident, Jia Tan stashed code hidden inside the repository, inside a random file supposedly used for testing. Then inside the tar release on the website (but left out of the repository) was a build script that would extract the code from that file and inject it into a different, highly sensitive program and leave a backdoor. Something that actually has very small echoes of what played out with ConfigLib, with code being left out of the repository but being sorta-present in the website release. Maltiez can't begin to do something like this with VS. Jia Tan had direct commit access and the ability to upload releases directly to the website, Maltiez doesn't. How about the University of Minnesota incident with the Linux kernel? Specifically their "Hypocrite Commits" paper, where they fixed some minor bug, but also smuggled in the beginnings of a vulnerability by breaking an assumption in a different part of the same code that was being fixed. This earned the whole university a lifetime ban from ever contributing to the Linux kernel again. This is much closer to what you're fearing, except that every one of em depended on C's memory unsafety, and they were incomplete holes. C# doesn't have those problems. Updated dependencies won't cause problems. Hidden behavior can only hide so much before it's obvious that you're up to no good, and really only languages like C can pack a small tweak that breaks big things in an unsafe way. And look at the portion of code that Maltiez is contributing to. It's primarily documentation, behaviorless declaration, and some thin layers of glue. I wrote it elsewhere, but if you're supposed to be doing 1 simple thing and instead you're scanning loaded assemblies and hashing them, that's gonna stand out. That's not going to slip past a review. Best he could slip past review is a completely untargeted crash that would be easily spotted and fixed. Human review of an untrustworthy actor's code is how we run the digital world right now.
-
There's really not a ton you can do to reduce the technical risk for the average person. In the end there's no substitute for code review, and the ModDB is explicitly unreviewed, as is every game's modding ecosystem. It's inherently reactive rather than proactive.
-
Technically not every game file, "Assemblies" in this context means "The DLLs (code) currently loaded by VintageStory". And yes, it never interacts with your PC's files. MKMoose got this one. I also have no idea what the source for that list of names is, but regardless it seems to be accurate and in the same order as they are in the code if anyone wants to spot check it. I only checked the first two, Aimbot (3606486923) and InstantShot (3515110866). Yes. It can do one of a number of many things. Rarely (0.565%), it'll spam random key presses, buttons, and mouse clicks every game tick. Very rarely (0.196%), your player will attack itself. The rest are various flavors and varieties of freezes, crashes, disconnects, and normal exits. There's two. The first one, MKMoose mentioned. That's the one that triggers in response to obfuscation or string matches. The other one is (5±4) * 107471, between 1 minute 47 seconds and 16 minutes. This one triggers if any of the types contain nonprintable characters in their name, I suppose another obfuscation check, but neither of the two false positive mods I inspected would have triggered this one... maybe the original cheat mod was using a particularly wacky kind of obfuscation that inspired this? No, the networking, UI, and other tomfoolery should only produce direct crashes and freezes. For the UI for example, your UI won't glitch out, instead it's is set up to be the trigger for the crash. It sets the list of GUI Composers to null, so the next time something goes to grab a Composer, it'll crash. There's some behavior I can't personally predict without testing it, one of the random options is telling the game client to Start() when it's already started. I'm not sure what exact effects that has, but I do imagine it's quite consistent, and most likely just crashes. Might also freeze. Based on what I read before giving up, I can't imagine it's subtle. Like I mentioned in the last one, it doesn't really hide or alter error logs. It leaves banana peels strewn in the main walkway and waits for someone to take themselves out. In all the logs I've seen so far, it's the game itself that trips over it rather than a mod. This also aligns with my expectations based on the code. However, it is still "blaming other mods" in that if you remove the mod that upset it (false positive or true positive), it will stop crashing. That does implicate the other mod, if not for being bad code, then for being incompatible in some way with another mod.
-
IMO, likely more than ~100. Really doubt we hit 1000 false positives just based on vibes. Downloads are cumulative across versions, they're not unique users. If we pretend the highest number of downloads on any single version is a proxy for unique downloads, it's 1200 for the both of them combined. Caves N Caverns likely has a substantial population of single player users. URL Radio sounds like it'd be almost completely multiplayer users. Just based on vibes still, let's say 650 (all of em) from URL and 250 (half) from CNC are downloads for servers. So that's 850 opportunities pulled straight out of my assumptions, however common ConfigLib is on your average server is what's going to matter for the final made up body count. I don't know enough about that to even try to guess though.
-
Welcome to the forums! Pr0fesseur's assessment is accurate. Right now we're aware of 2 mods that were caught in the crossfire, the caves n caverns you mentioned already and the url radio mod.
-
Ah no need to apologize, we're saying the same thing. I didn't spot your answer to that part of genderBiohazard's question when I read it through the first time.
-
They didn't specify which part of the community is the part engaging in bad faith, but I'm going to risk putting words in their mouth and say I don't believe Mushroomancer thinks this is it.
-
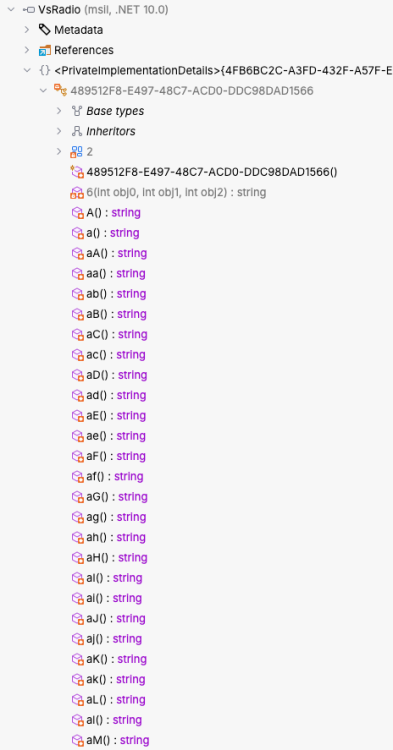
Two mods that I'm aware of. Caves N Caverns, as already mentioned. URL Radio is the other one that's confirmed. I'd be very interested to investigate any other mods. You can get hard proof for yourself with a decompiler. If you decompile a mod's DLL files and find any with a bunch of classes, functions, and variables with 1- and 2-letter names, it's obfuscated, and it would have angered ConfigLib. There are effectively no other ways to accidentally activate it. They don't all need to be short variable names, but about 22% of them need to be. Maltiez was targeting a specific modder, the creator of the paid cheat mod.
-
Undeniably caustic. Being caustic is externally viewable. Repentance comes from within. What (if anything) would you (@anyone) accept as a genuinely repentant Maltiez? Would it even make a difference if he was somehow verifiably repentant? It's fine if there's nothing and if it makes no difference, just trying to understand better. No worries, horse isn't going anywhere. Welcome to the forums!